Penetration Testing
Manual testing of web applications, APIs and external and internal networks: we try to jump your fence before someone else does.
YOU GET: REPORT · RETEST · ATTESTATIONCybersecurity for growing businesses
We test, monitor and harden your digital perimeter, mark every weak point in red and help you close it, so no one jumps the fence.
Services
Manual testing of web applications, APIs and external and internal networks: we try to jump your fence before someone else does.
YOU GET: REPORT · RETEST · ATTESTATIONContinuous scanning, risk-based prioritisation and tracked remediation, so the holes in your fence get fixed in the right order.
YOU GET: MONTHLY RISK REPORTArchitecture and configuration review of networks, firewalls and cloud accounts against CIS benchmarks.
YOU GET: PRIORITISED FIX PLANLog monitoring and alert triage on SIEM platforms such as Splunk and Elastic. We see someone at the fence before they reach the house.
YOU GET: TRIAGED ALERTS · MONTHLY REVIEWHypothesis-driven hunts mapped to MITRE ATT&CK, plus OSINT and dark-web monitoring of what attackers already know about you.
YOU GET: HUNT FINDINGS · EXPOSURE BRIEFContainment, investigation and recovery when someone gets over the fence, followed by a clear post-incident report.
YOU GET: CONTAINMENT · ROOT CAUSE · LESSONSA part-time security lead for companies without one: strategy, policies, risk register, board reporting and vendor reviews.
YOU GET: ROADMAP · MONTHLY BOARD BRIEFGap analysis, ISMS build-out and audit readiness for ISO/IEC 27001, NIS2, DORA and SOC 2.
YOU GET: GAP REPORT · AUDIT-READY EVIDENCEWe check, fix and document the controls insurers now require — MFA, EDR, tested backups, an IR plan — before your application or renewal.
YOU GET: CONTROL EVIDENCE PACKCompliance
Regulation decides most security budgets. We map what applies to you and get you audit-ready.
How we work
We map your assets, users and attack surface.
Every weak point marked in red and ranked by business risk.
We close the gaps with your team, highest risk first.
Ongoing monitoring and retesting, so the fence stays whole.
Reports
Every finding states what it is, why it matters to the business and exactly how to fix it. No 200-page scanner dumps.
The perimeter is in reasonable shape, but we found one realistic route inside the network: an unpatched VPN appliance, made worse by weak MFA enforcement on Microsoft 365. Both can be fixed within a week with existing tools and no new spend.
p=none, so spoofed emails using your domain are not rejected.p=quarantine, then p=reject after monitoring reports for two weeks.Industries
DORA, client data, payment systems.
Patient data, connected devices, uptime.
SOC 2, ISO 27001, customer security reviews.
Web apps, payments, account takeover.
Confidential files, email fraud, client trust.
Ransomware resilience, supply chain, NIS2.
Engagements
Every engagement is scoped to your size and risk, and quoted on request.
A complete walk of your perimeter.
We keep watching after the test.
Security leadership, part-time.
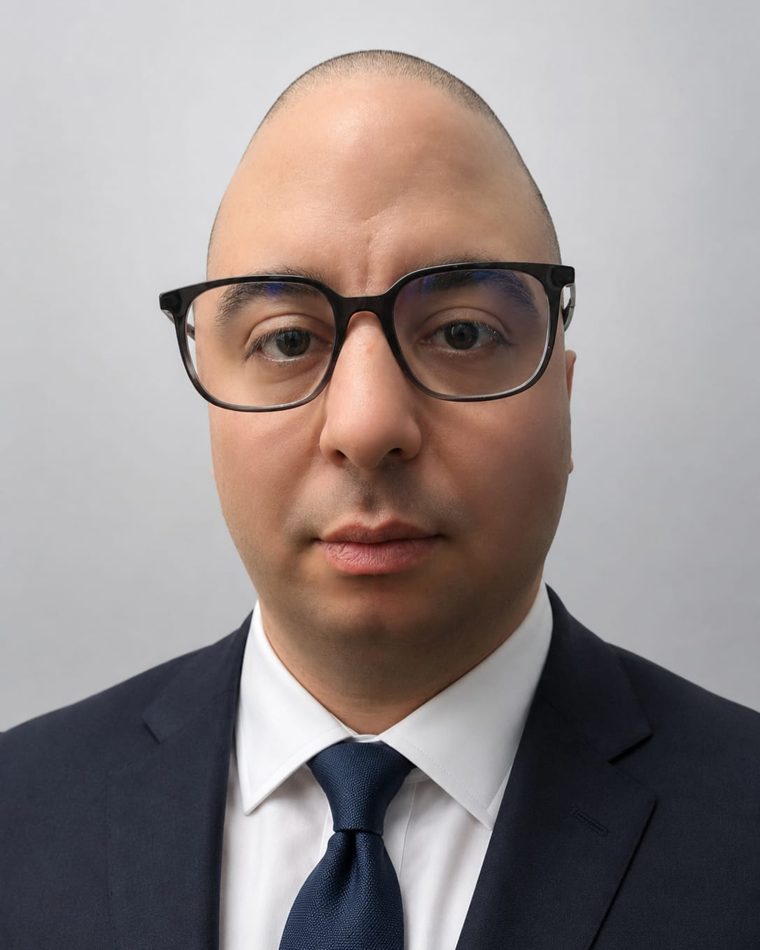
Who you work with
HUGO CUNHA · FOUNDER & PRINCIPAL CONSULTANT
Hugo spent more than twenty years on the building side of technology: network engineering, IT infrastructure, web server administration and software development, including roles at Microsoft and Apple in Cambridge, UK, and Virgin Media.
He founded Yard Lab to bring that builder's view to defence. Knowing how systems are put together is the fastest way to see where they come apart, and to explain the fix in terms the people running them will act on.
Questions
A free 30-minute scoping call. We then send a written scope and fixed quote. Nothing is tested or monitored until scope and written authorisation are signed.
A ten-person office and a fifty-site manufacturer need very different work. We quote against your actual scope, as a fixed price, so there are no surprises.
Tests are planned with you, run in agreed windows and paused immediately if anything looks unstable. You always know what is being tested and when.
Yes. We work remotely with clients across the EU, UK and US, and align to the frameworks that apply where you operate.
Client data is handled under NDA, stored encrypted in the EU, kept to the minimum needed and securely deleted at the end of the engagement.
Go to Report a breach. Don't switch systems off or wipe anything yet — evidence matters.
Incident response
Email: incident@yardlab.net — put “INCIDENT” in the subject
Include your name, organisation, a call-back number and a short description of what you are seeing. We will reply as fast as possible.
Triage and scoping, containment, evidence preservation, investigation of root cause, recovery support, and a clear post-incident report with lessons and fixes.
Security & privacy
We practise what we sell. If you find a security weakness in yardlab.net or any system we operate, we want to hear from you.
Email security@yardlab.net with a description, the affected URL or system, steps to reproduce and any proof of concept. Our contact details are also published in security.txt.
Last updated November 2026
Yard Lab is the controller of personal data collected through this website. Contact: privacy@yardlab.net.
To reply to your request and prepare a proposal (steps prior to a contract, Art. 6(1)(b) GDPR) and, where you have ticked the box, your consent (Art. 6(1)(a)).
We use a small number of trusted providers for website hosting, email and form handling, each bound by a data processing agreement. We do not sell or share your data for marketing.
Enquiries that don't become clients are deleted after 12 months. Client records are kept as long as the law requires.
You can ask to access, correct, delete, restrict or port your data, or object to its use, by emailing privacy@yardlab.net. You may also complain to your national data protection authority.
Contact
Tell us about your organisation. We'll reply with next steps and a time for a free scoping call.